Contact

SOC, Executives & Investigations

Custos

Security teams and investigators

[ CST ]

Custos brings the asymmetric defense behind Mutin.ee to the security team: the exposed perimeter mapped before an attacker finds it, a signal the SOC can act on, executives covered without noise, and investigations that end in answers.

Perimeter · Activation · Analysis · Response · Evolution

Engagement

Feed

Synapse intelligence, delivered into the stack you already run.

Delivery
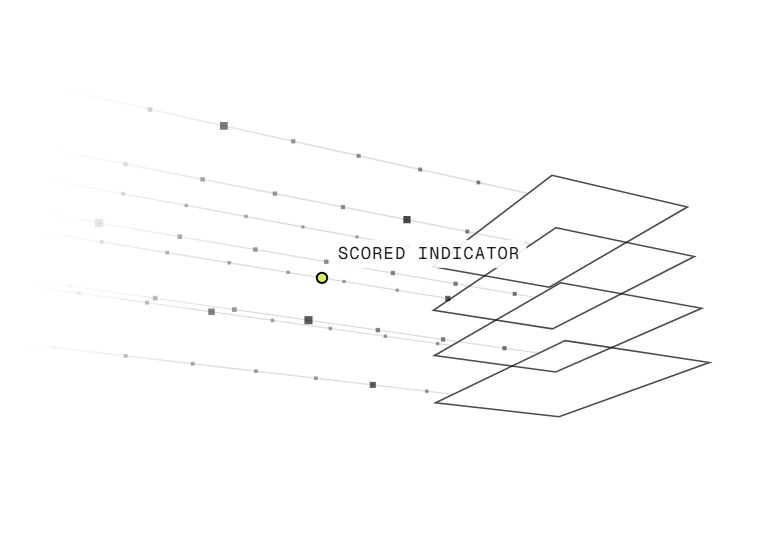
IOC feed for SIEM and SOAR, STIX/TAXII, REST API
Integrations
Recorded Future, Anomali, ThreatConnect, MISP
Content
Lookalikes, phishing kits, compromised credentials, actor activity
Deliverable
Validated, scored indicators

Retainer

The immune system on call: monitoring, response and removal.

Scope
Perimeter, executives, brand and SOC signal
Response
Notification, removal or escalation to SOC and legal
Cadence
Continuous, with quarterly rule evolution
Deliverable
Shared dashboard and monthly review

Investigation

When the question is who, how and how far.

Scope
Infrastructure and actor profiling, third-party due diligence
Method
In-depth open-source analysis, human-led
Output
Attribution to legal entities where evidence allows
Deliverable
Dedicated investigative report

System online

Live view

One intelligence pool, four points of contact with the world.

Capabilities

01/06

Perimeter Defense

The exposed surface mapped before someone else finds it: attack surface, lookalike domains, social and app-store abuse, with assisted removal.

Five phases, one perimeter to the next

01 Perimeter

Define what to protect.

Assets, brands, people and entities to observe or investigate are agreed and scoped.

02 Activation

Point Synapse at it.

Searches and alert rules are configured on Synapse against your perimeter.

03 Analysis

Human judgment on every signal.

Analysts validate signals and prioritize them by real risk, not by volume.

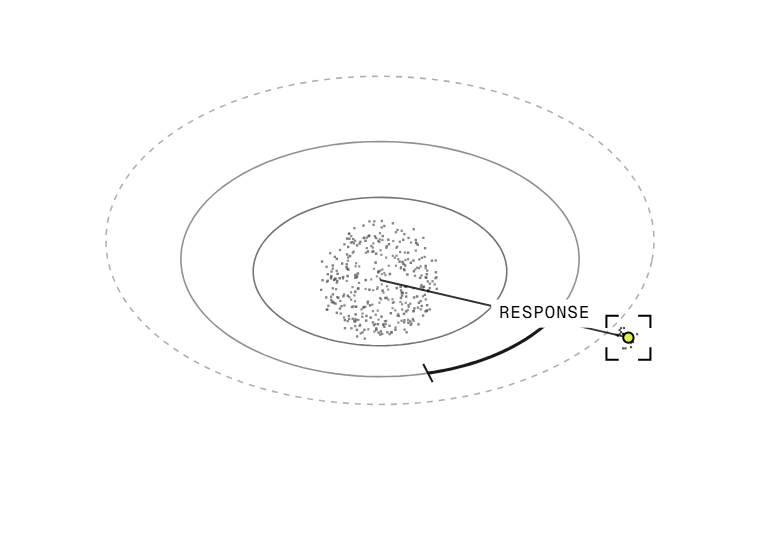
04 Response

Act, or hand over.

Notification, removal, or escalation to the SOC and legal team, documented end to end.

05 Evolution

The system learns.

Rules, perimeter and capabilities are refined continuously. The client decides where to stop.

Answers,
not alerts.

Frequently asked questions

Through an IOC feed integrable with SIEM and SOAR, STIX/TAXII exports, a REST API, and native exports to Recorded Future, Anomali, ThreatConnect and MISP.

The intelligence pool behind every Mutin.ee capability. It continuously cross-references open, closed and underground sources to map digital exposure and detect illegal activity in near real time.

Mutin.ee analysts. Signals are validated and prioritized by real risk before they reach your team, so the SOC receives context rather than volume.

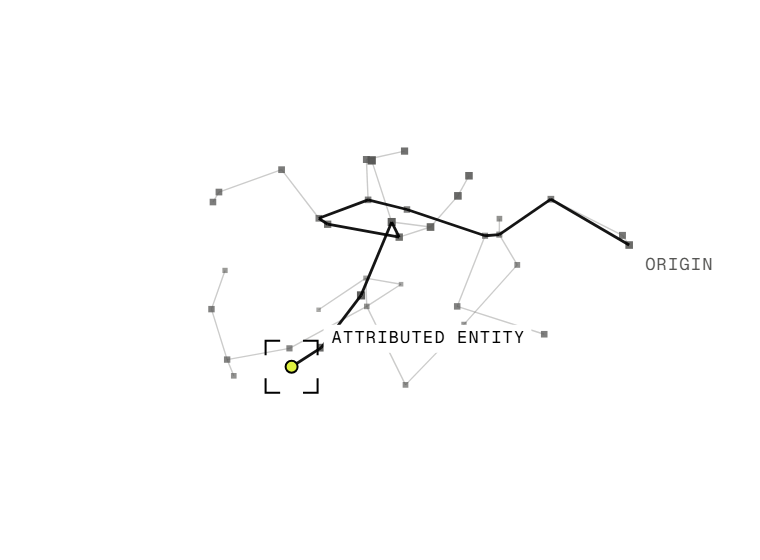
In authorized investigations, yes. Digital identifiers are correlated with corporate registries and court records to attribute operations to legal entities, supporting law-enforcement referrals.

Perimeter definition and activation typically take days, not months. The engagement can start with a single capability and extend from there.

Next

Watchtower